Why it exists
A container image needs evidence about what it includes and whether the artifact being verified is the one that was built.
Portfolio / CASE STUDY
Private security lab
A reproducible container security lab that builds, scans, inventories, and signs a small Go service.
Independent container security and verification
A container image needs evidence about what it includes and whether the artifact being verified is the one that was built.
I used a minimal Go service to compare an intentionally noisy baseline with a hardened image, generate a software bill of materials, and verify a signature against the saved artifact.
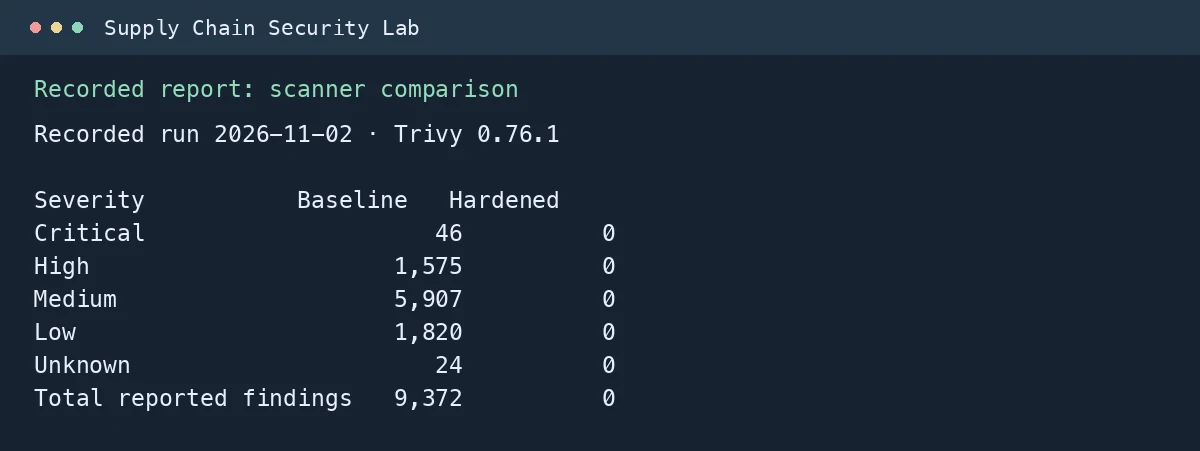
The lab records the scanner version and database for its baseline and hardened scans so the reported difference has context.
A CycloneDX SBOM captures what the scanner identified in the built image for later inspection.
The signing workflow ties verification to the saved artifact and checks it after the local registry is stopped.
Private lab on a small service and recorded scanner database. Results are specific to the artifacts and configuration that were tested.
Private repository supply-chain-security-lab